For years, privacy advice rested on a single principle: keep your data separated. Your bank details lived in one app, your messages in another, your browsing behind its own walls. The comfort came from the fact that these silos rarely spoke to each other. A tracker that reached one rarely reached the rest.
That separation is dissolving. A new layer of AI tooling now sits above your individual apps, reading across all of them at once — and in doing so, it removes the very walls that used to contain a leak. This article explains what these "Layer Zero" assistants actually do with your data, how a new category of exposure called Contextual Data Exhaust forms, why the privacy tools most people trust cannot see it, and where the risk can realistically be reduced. As in the rest of this series, the limits of any defense are stated plainly rather than oversold.
What "Layer Zero" changes about your data
The term describes AI-native interfaces that float above your existing apps and websites rather than living inside any one of them. Instead of opening a travel site, a calendar, and an email client separately, you ask an assistant to handle the task, and it reaches into all three on your behalf.
To function, these assistants need persistent, multi-modal access. They pull dates from your chats, details from your emails, and preferences from your history, then act across services to complete a request. The value is obvious. So is the structural change underneath it: your entire digital identity now flows through one connected pipeline instead of many isolated ones.
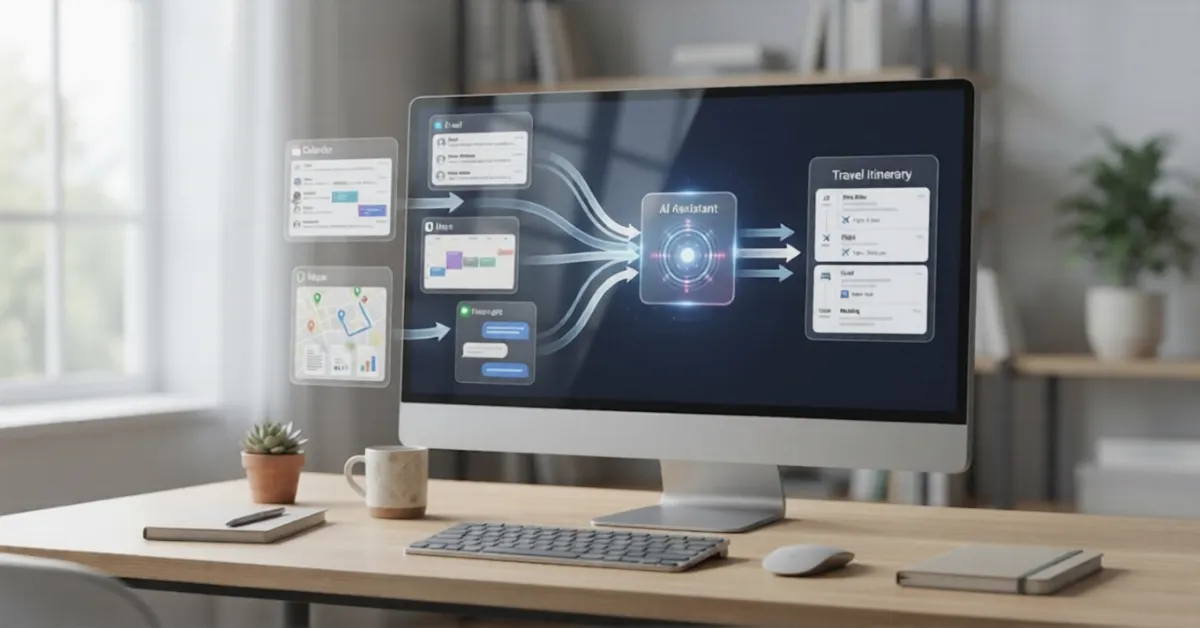
That consolidation is the core shift. When data was fragmented, a single exposure was contained. When one system reads everything, a single point of access exposes far more than any individual app ever could.
Contextual Data Exhaust: the new leak
The distinct risk here is not any single piece of data. It is the context between pieces of data — what an assistant assembles when it combines several sources to fulfill one instruction.
Consider a routine request: build a vacation itinerary. To complete it, the assistant does not simply look up a flight. It reads your travel preferences, your budget, your family contacts, and your recent browsing. The output is a plan, but the byproduct is a detailed, synthesized picture of your intent — assembled in one place, at one moment. This byproduct is what can be called Contextual Data Exhaust.
The important detail is timing. This picture forms before you act. The itinerary exists, and the intent behind it is fully articulated, well before you book anything.
How AdTech follows agent activity
Advertising networks and data brokers have already begun shifting focus. The older model tried to infer intent from cookies and page visits after the fact. The agentic model offers something more direct: the plan itself, spelled out.
By observing the API calls an assistant makes to gather data, trackers can map an entire intent cycle. They are not guessing what you might want based on scattered signals. They are watching the exact plan being synthesized on your behalf. The distinction matters — prediction becomes observation, and observation is far more accurate.
Cookies revealed where you had been. Agent activity can reveal where you are about to go, and why, before you have committed to going there.
Why standard defenses miss this
The privacy tools most people rely on were built for a browser-and-app world. Against agentic activity, they have three specific blind spots, and each is worth understanding rather than accepting on faith.
| Defense you trust | Blind spot | Why it misses the leak |
|---|---|---|
| Conventional ad blocker | The agent acts as a proxy | Requests are made from the assistant's own servers, not your device, so there is no local request to inspect |
| Anti-tracking extension | Extraction is semantic, not visual | It monitors the meaning of the data an assistant receives, so there is no pixel or script to catch |
| Platform permissions | The platforms are opaque | Proprietary systems give little granular control over which agent touches which data source |
The pattern is consistent with earlier articles in this series: these tools are not broken. They simply guard a layer the exposure no longer passes through.
Where the risk can actually be reduced
Reduce the problem to its foundation and one dependency stands out. The exposure forms at the moment separate data sources are merged into a single synthesized context. If that anomalous assembly can be recognized and interrupted, the exhaust never fully forms.
This is the layer Total Adblock is built to address as the web moves toward agentic activity. Rather than watching only for suspicious URLs, its Intent-Based Protection applies semantic filtering — monitoring the nature of the data an AI layer requests, not just its destination. The logic follows a direct chain:
- If an unauthorized agent attempts to combine your calendar data with your location history, the request is examined for that pattern.
- If the combination matches an anomalous contextual assembly, the link is severed before the sources merge.
- If the sources never merge, there is no synthesized intent to observe or extract.
The limit deserves the same honesty as the earlier pieces. This approach interrupts unauthorized contextual assembly going forward; it does not reach into a proprietary platform's servers and delete context it has already processed, nor does it rewrite how a closed system handles your data internally. Its function is to close the path forward — which, against activity designed to synthesize continuously, is the path that counts. And because the filtering targets anomalous assembly rather than legitimate requests, the assistants you deliberately authorize continue to work as intended.
Keeping your context your own
The unsettling quality of agentic surveillance is how ordinary it feels. You asked for help with a trip. Nothing looked suspicious. Yet in fulfilling that one request, a system read across your accounts and assembled a picture of your intentions more complete than any cookie ever captured — and did so before you acted on it.
The practical response is not to abandon AI assistants or treat every one as hostile. It is to stop treating them as neutral tools. They are powerful data-processing engines, and without containment, the same capability that serves you can serve as an informant. The goal is straightforward: decide what context an agent may assemble, and interrupt the assembly you never authorized.
Deciding what your agents can see — and when they can act — is how you keep convenience from quietly costing you your privacy. Take back control of your AI workflow by implementing Total Adblock's semantic protection today.